
CVE-2021-26855 is a server-side request forgery (SSRF) vulnerability in Exchange which allowed the attacker to send arbitrary HTTP requests and authenticate as the Exchange server.
0-day vulnerabilities were detected at On-premise version of Microsoft Exchange server. Chain of vulnerabilities CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, CVE-2021-27065 were exploited in chain attack by state-sponsored, operated from China group. Exchange servers all around the world were attacked. Cloud version of Exchange is not affected. Check below example of CVE-2021-26855 vulnerability exploitation.
Microsoft HAFNIUM Attack and vulnerabilities details – https://www.microsoft.com/security/blog/2021/03/02/hafnium-targeting-exchange-servers/
CVE-2021-26855 exploitation example
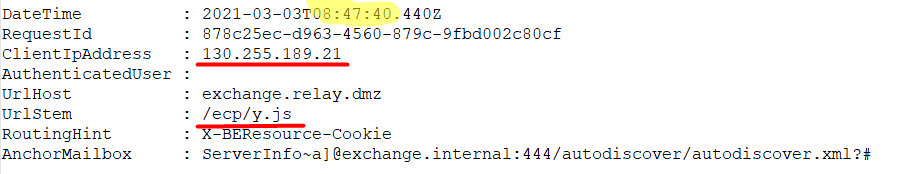
CVE-2021-26855 HTTPProxy log example

CVE-2021-26855 Command & Control (IP:130.255.189.21) server connections
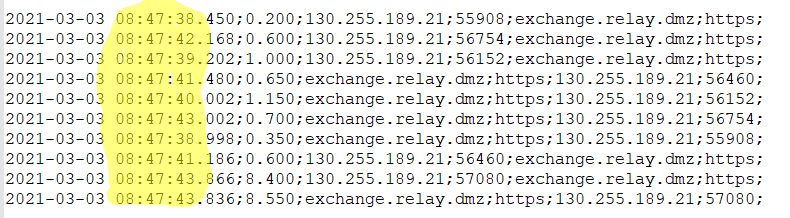
Exploited vulnerabilities in attack chain: CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, CVE-2021-27065
Indicators Of Compromise (IOCs)
| Type | Indicator |
|---|---|
| IPv4: | 139.59.56.239 |
| IPv4: | 86.105.18.116 |
| IPv4: | 130.255.189.21 |
| URL: | /ecp/y.js |
| User Agent: | python-requests/2.25.1 |
Mitigation:
US-CERT Exchange 0-day vulnerabilities – https://us-cert.cisa.gov/ncas/alerts/aa21-062a
Volexity Exchange 0-day vulnerabilities – https://www.volexity.com/blog/2021/03/02/active-exploitation-of-microsoft-exchange-zero-day-vulnerabilities/